EMERGENCY
Cyber
• Sep 29, 2026
Cyber Resilience Foundations - See it, Stop it, Recover from it.
The three foundations of cyber resilience, and the questions worth asking about each. No single tool makes an organization resilient. It comes from getting three things right: seeing an attack early, stopping it fast, and recovering when something gets through. This issue covers all three.
-
See it: SIEM & SOC
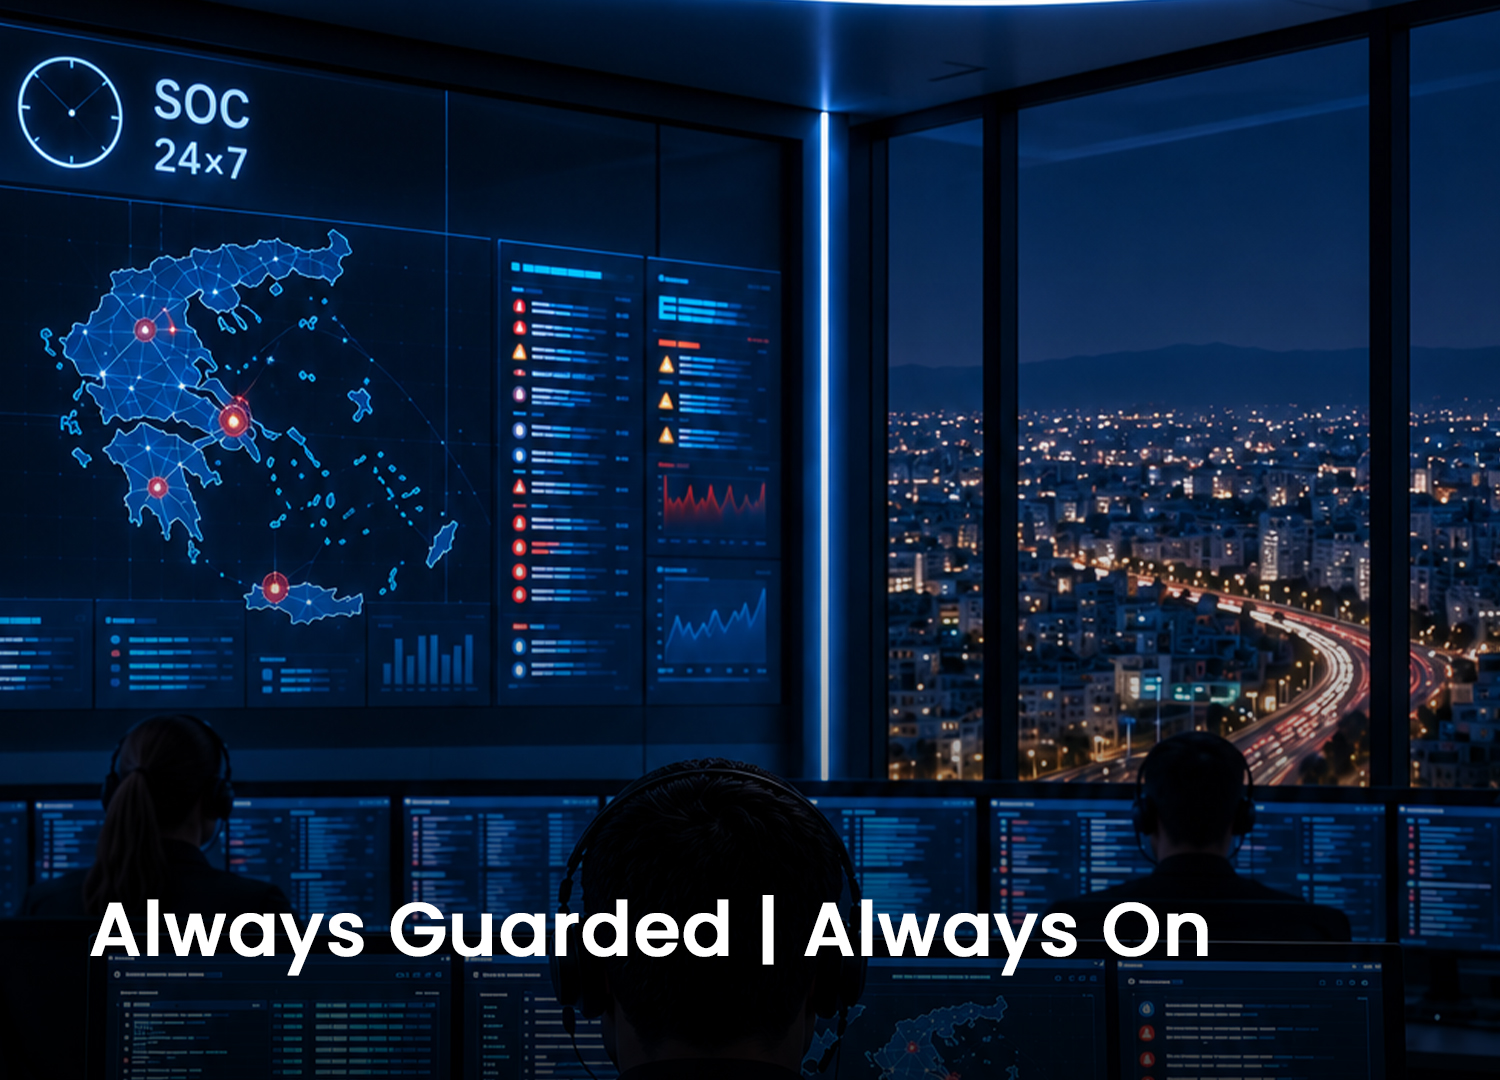
You can't defend against an attacker you can't see. On average it takes around 200 days just to identify a breach, and the attacker spends that time moving quietly through the network and getting ready. The problem is rarely too few alerts. Most teams have too many. Logs sit scattered across dozens of systems with nobody correlating them, alerts fire at 3am when no one is watching, and the real threats get lost among thousands of false alarms. Our Athens-based SOC brings every signal into one place, correlates it, and has people watching it 24x7. A real threat shows up in minutes, not months later in an incident report.
If an attacker were inside your network right now, how long before you knew?
-
Stop it: MDR & Incident Response
Seeing a threat is half the job. The other half is stopping it before it spreads. Attacks that used to take days now take hours, and an attacker can get from one foothold to encrypted systems in a single afternoon. A good response needs someone available the moment an alert fires, the experience to tell a real incident from noise, and a plan that has been rehearsed before it's needed. Our Managed Detection and Response service does more than raise the alarm. We isolate affected systems and contain the threat so a small incident doesn't turn into a company-wide one.
When something triggers at 3am, who responds, and how fast?
-
Recover from it: Backup & Disaster Recovery
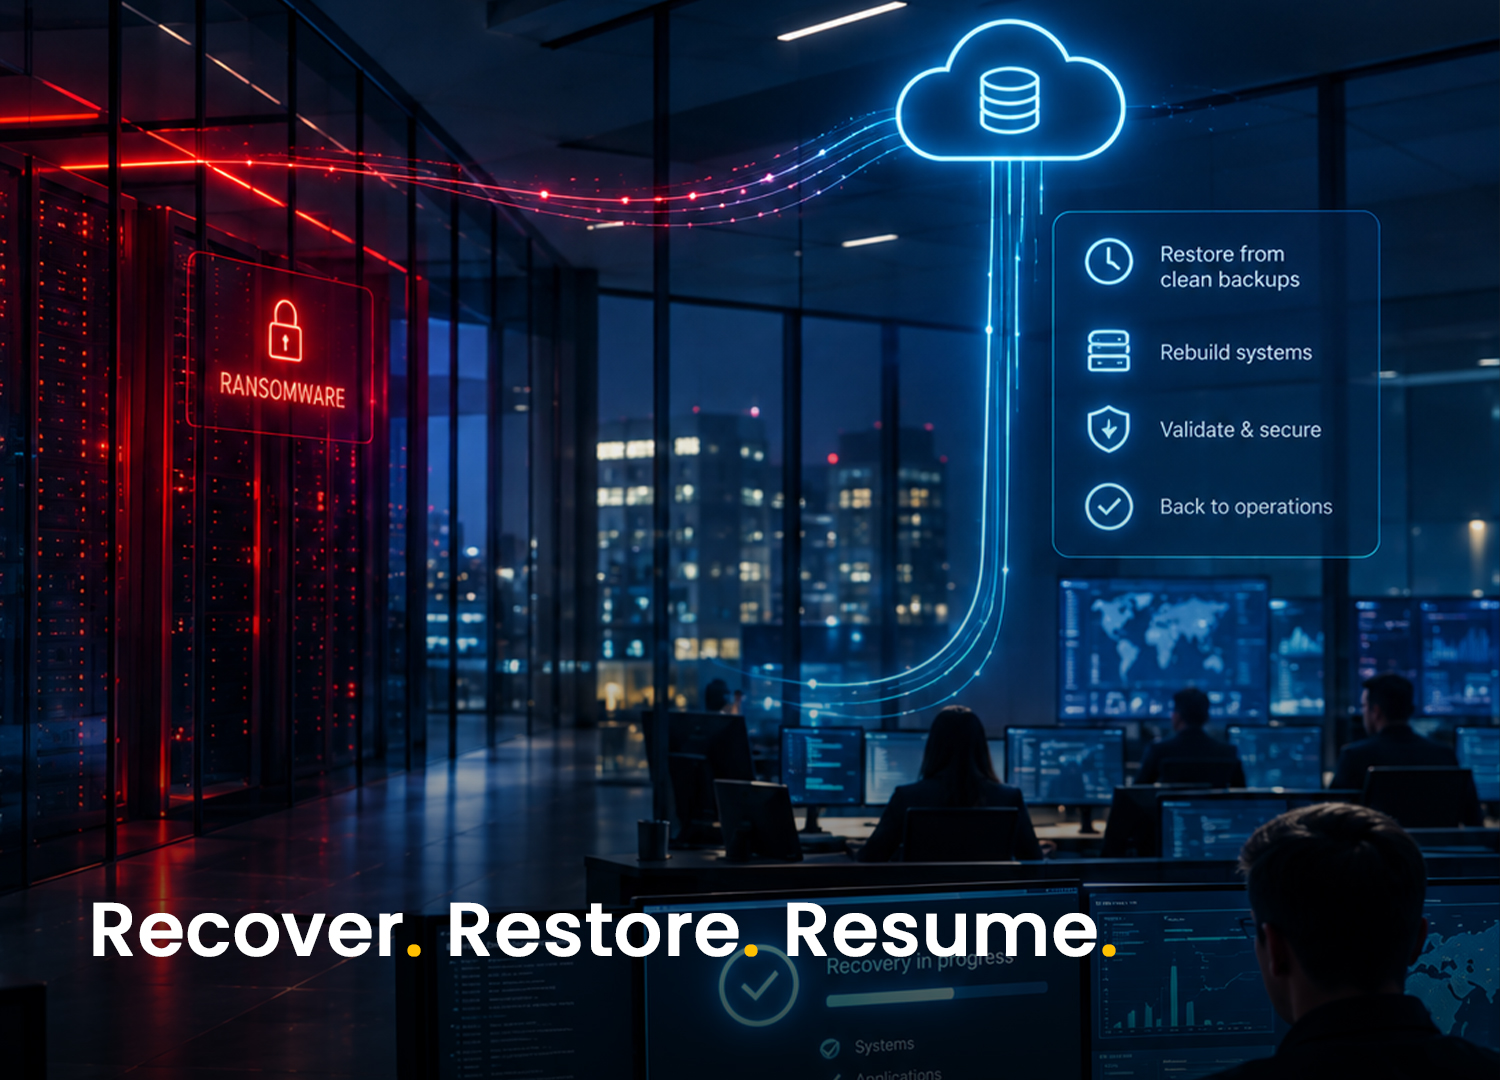
Sooner or later, something gets through. The organizations that come out of an attack intact are the ones that were ready to recover. When ransomware hits, the questions come fast. How recent is the last clean backup, and has anyone tested whether it restores? Will you be running again in hours or in weeks? Can you recover without paying? Paying a ransom doesn't guarantee you get your data back. A tested recovery plan does. We help organizations put one in place, with protected backups, clear recovery targets, and a plan that's been tested before the day it's needed.
If your critical systems went down tomorrow, how long until you were running again?
Where do you stand?
If any of these questions was hard to answer, let's talk. Our team can assess your detection, response, and recovery readiness and show you where the gaps are.
Talk to our expertsRead Next
Sep 22, 2026
2 awards at the BITE Awards 2026
Jul 21, 2026
Smart Greenhouses: The Sensors Are the Easy Part
Start your journey
Our team of seasoned experts is dedicated to delivering tailored solutions that perfectly align with your specific business needs and objectives. Do you want to help you navigate your path to success?